

 University
We bring SBOM, artifact signing and DevSecOps into the pipelines you already use. Our management system is ISO/IEC 27001, 27017 and 27018 certified.
Supply chain security protects the software lifecycle from vulnerabilities, malicious code and compromises, from writing the code to production. SparkFabrik is an AI Native Engineering company that brings these controls into client pipelines and is a member of OpenSSF and Linux Foundation Europe.
The Cyber Resilience Act, the NIS2 directive and the DORA regulation require it too. Our compendium on NIS2 and DORA explains how to bring cloud native applications and the supply chain into line. Our approach is security enablement: controls help developers, they do not stop them.
An SBOM for every build lists components and dependencies: when a vulnerability comes out you know at once whether it affects you.
Scans, artifact signing and policies run in the pipelines you already have, from commit to deploy.
Policies, attestations and reports to prove compliance with the Cyber Resilience Act, NIS2 and DORA.
Since 2015 we have brought secure, compliant delivery processes into enterprise organizations. We work inside the development flow you already have.
SAST and dependency analysis (SCA) in the development flow, from the first commit, with tools such as SonarQube and Snyk.
Automated controls in CI/CD pipelines, on GitLab or GitHub Actions, to catch supply chain threats.
Security policies with Open Policy Agent (OPA) on build and deploy, artifact signing with Sigstore: auditing, access, compliance.
Automated policies, secure templates and verified software catalogs inside the development platform, Backstage included.
Image scanning with Trivy, vulnerability management and container hardening.
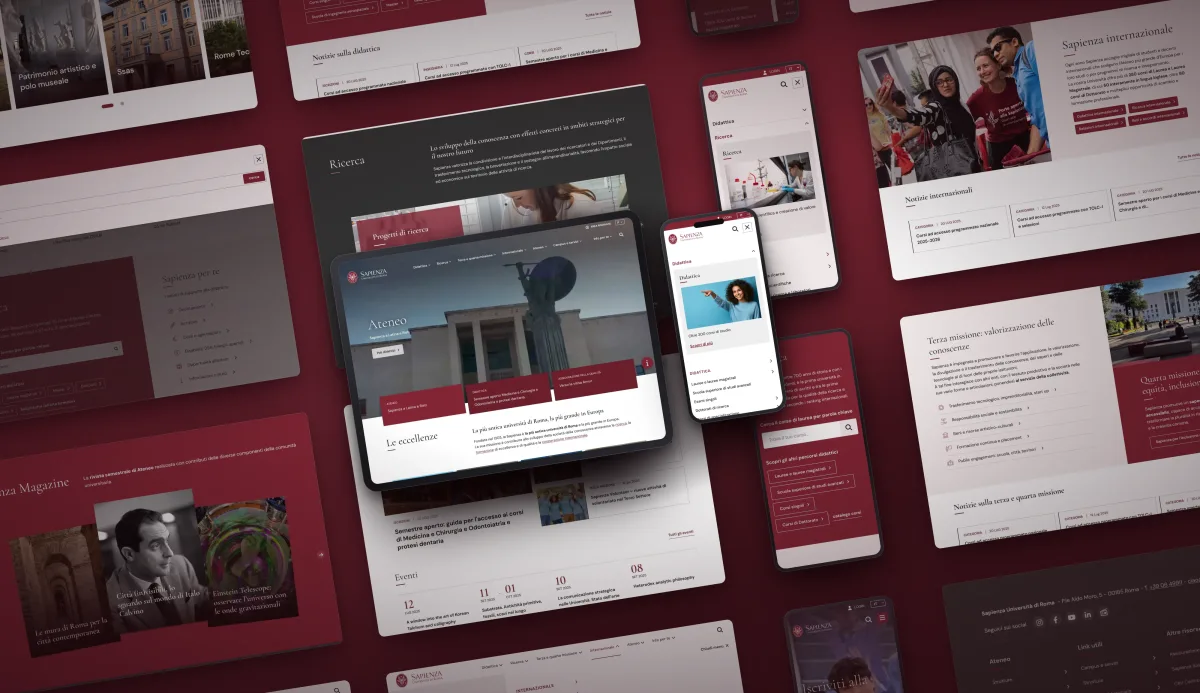
University
 University
−70% in content publishing time
 Publishing


We apply to ourselves what we recommend: our management system is certified ISO/IEC 27001, 27017 and 27018 for the design and development of software and the management of cloud platforms. Certificates issued by Scandinavian Certification, accredited by Norwegian Accreditation.

Information security management system (ISMS).

Security controls specific to cloud services.

Protection of personal data (PII) processed in cloud services.
The certification covers the company management system, not individual products or services.
From risk assessment to continuous monitoring.
Assessment workshops and supply chain risk analysis, with a roadmap of interventions.
We integrate controls and tools into existing pipelines, one step at a time, without slowing releases down.
Best practices, compliance management, continuous monitoring and reporting.
AI correlates vulnerabilities, context and real exposure; a person on the team decides what to fix first.

The challenges, the attacks and the defense strategies.
Download the guideAbout supply chain security.
Yes. AI correlates vulnerabilities, context and real exposure, so the team sees first what matters; a person decides what to fix and when. The checks live in the pipelines you already use and the rules stay in your repository.
An SBOM (Software Bill of Materials) is a complete inventory of all software components and dependencies. It matters because it:
We generate SBOMs in standard formats (SPDX, CycloneDX) integrated into CI/CD pipelines.
For Drupal sites we use DruBOM, our open source module that generates the SBOM of the site, useful for the Cyber Resilience Act. The steps are in our article on generating the SBOM of a Drupal site with DruBOM.
SLSA (Supply-chain Levels for Software Artifacts) is an OpenSSF security framework. Since version 1.0 its levels are grouped in tracks. The Build track has four levels:
Version 1.2 adds the Source track, with levels from Source L1 to Source L4 for source code.
We help companies achieve increasing SLSA levels based on their security needs.
SparkFabrik is a member of the Open Source Security Foundation (OpenSSF), and its management system is certified ISO/IEC 27001, 27017 and 27018. It protects the software lifecycle of Italian and European organizations from design to production: SBOM, vulnerability scanning, code signing and SLSA compliance in CI/CD pipelines.
Integration occurs at multiple pipeline stages:
We use tools like Trivy, Syft, Cosign, Kyverno to automate all checks.
Investment depends on environment complexity:
The investment often comes from a regulatory obligation (NIS2, DORA, CRA). We discuss it in a first conversation, with no commitment.
Tell us which pipelines you use and which regulations apply to you. We will tell you which control we would start with.
Tell us about your projectUpdated
Services
Resources